QE-AI2025Product Engineering · Application SecurityOct 20, 2025
QuickEats
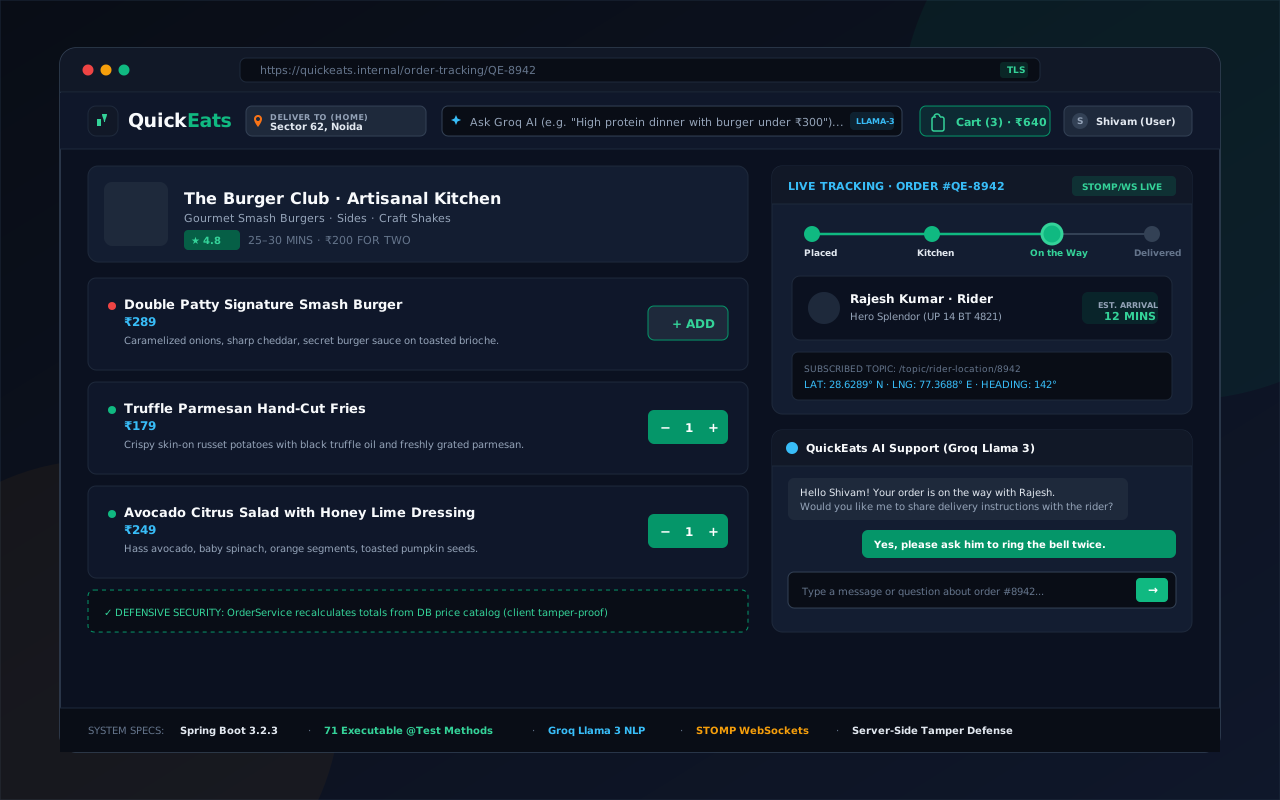
AI-assisted product engineering and application security system. Highlights include server-side price recalculation, ownership validation, JWT refresh-token rotation, real-time STOMP order updates, and conversational AI assistance. Verified with 71 executable @Test methods across 23 backend test classes.
Technologies
Product EngineeringApplication SecuritySpring Boot 3WebSocketsGroq Llama 3PostgreSQL
Executive Summary
QuickEats is a food ordering and delivery backend engineered to solve critical application security risks and real-time state synchronization challenges.
Project Context & Core Attributes
- Problem: Online food delivery platforms face cart manipulation (tampered client prices), unauthorized order access (IDOR vulnerabilities), and fragile multi-user order tracking.
- Intended User: Food delivery platforms, restaurant networks, and mobile ordering apps requiring tamper-proof transactions.
- My Role: Backend systems architect and security engineer (data modeling, Spring Security configuration, WebSocket integration, and automated security test suite).
- Solution: High-performance Spring Boot 3 backend featuring server-authoritative price recalculation (strictly ignoring client-supplied amounts), strict account-level ownership validation, JWT refresh-token rotation, and bi-directional STOMP WebSockets for live status updates.
- Verified Status: Backend architecture verified through 71 executable @Test methods across 23 backend test classes covering security controls, price recalculation logic, IDOR protections, and database transactions.
- Evidence: Open-source repository with full test suite at github.com/shivam-shukla888/QuickEats-Ordering-System.
Key Engineering Lessons & Security Mechanisms
- Server-Side Price Recalculation: The order service strictly ignores client-supplied item prices. Total amounts are calculated exclusively on the server by looking up authoritative database prices, preventing cart tampering attacks.
- Ownership & IDOR Validation: Strict entity-level ownership validation guarantees that customers can only view, modify, or track orders tied to their authenticated account.
- JWT Authentication & Refresh Token Rotation: Implements stateless short-lived JWT access tokens paired with database-backed refresh token rotation and revocation.
- Real-Time Order Updates: Bi-directional STOMP WebSockets over SockJS broadcast order lifecycle progression (PENDING ➔ PREPARING ➔ OUT_FOR_DELIVERY ➔ DELIVERED) and live simulated delivery coordinates.
- Conversational AI Assistance: Groq API (Llama 3) powers conversational food recommendations and customer support grounded in verified order context.
- Verified Automated Test Suite: Backed by 71 executable @Test methods across 23 backend test classes covering security controls, price recalculation logic, IDOR protections, and database transactions.
Architecture & Implementation Stack
- Backend: Spring Boot 3.2.3, Java 17, Spring Security 6, JJWT
- Persistence: PostgreSQL, MySQL 8, and Hibernate ORM
- Real-Time: Spring WebSocket with STOMP and SockJS
- AI Integration: Groq API (Llama 3) for contextual menu assistance
Questions about this project?
Feel free to reach out if you'd like to talk about the tech stack, implementation, or a similar project.
← Back to Projects
EXPLORE:Services →